Automation Governance Is the Reliability Layer for Small Businesses
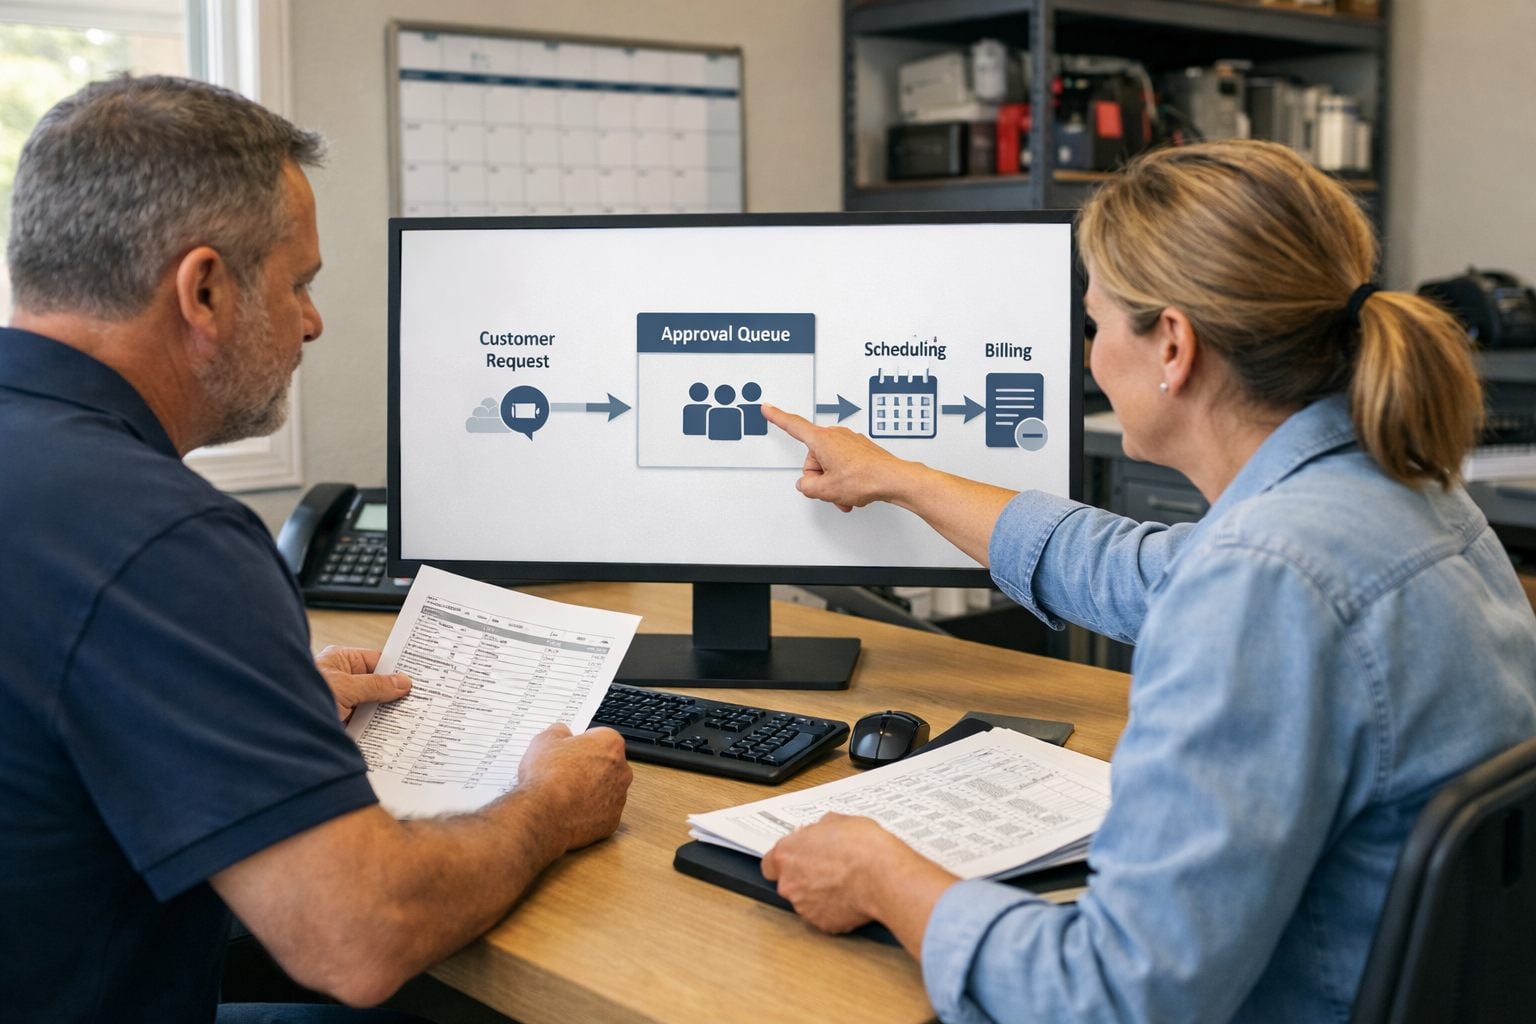
That operational value needs a control layer. Automation governance for small businesses is the practical operating system around a workflow: it defines what the workflow may do, where it must stop for a person, how its actions can be reconstructed, and who takes charge when the result is wrong.
It is not enterprise bureaucracy. A small business does not need a committee to let a workflow tag a new lead or draft an internal handoff. It does need a clear boundary when that same workflow can edit a customer record, send an appointment message, adjust inventory, or initiate a payment-related action. The right amount of governance rises with the access granted, the consequence of an error, the ease of undoing it, and the sensitivity of the data involved.
- Permissions set the workflow’s allowed actions: read a schedule, for example, rather than edit every customer record.
- Approvals create a deliberate stop before consequential actions, such as sending a refund or changing a booked job.
- Audit trails preserve the trigger, data used, action taken, result, and approver so a decision is explainable, not merely logged.
- Named ownership assigns one person to the business outcome and another, where needed, to fix exceptions or roll back errors.
- Monitoring and review expose failed runs, drift, and recurring edge cases, then turn those findings into workflow improvements.
An unmanaged automation is often fast until it fails: credentials are shared, decisions are invisible, and an unusual request has nowhere to go. A governed workflow has a defined scope, a visible record, and an accountable responder. That difference preserves speed while keeping operational control with the business.
Start With a Simple Risk Tier: Access, Impact, Reversibility, and Data
A workflow that applies a “new web lead” tag and one that changes a technician’s pay rate may both be triggered by a form submission, but they do not deserve the same operating freedom. Use a four-factor screen to place each workflow in a risk tier: access (the systems, permissions, and records it can reach); impact (the operational, financial, or customer consequence of a bad action); reversibility (how completely and quickly the action can be undone); and data (whether it handles sensitive customer, employee, financial, or business information).
| Tier | Typical workflow | What changes the control level |
|---|---|---|
| Low | Tagging an inbound lead, routing a task internally, or drafting an internal job summary | Limited read access, no external communication, and an easily corrected result |
| Medium | Updating inventory quantities, creating a customer-record note, or preparing a customer message for review | Edits affect operations or customer service, but a person can identify and correct the change |
| High | Issuing refunds, changing payroll details, sending commitments to customers, modifying account access, or making broad system updates | Financial authority, external effects, sensitive data, broad permissions, or damage that is difficult to unwind |
Reversibility is often the deciding factor. Removing an incorrect lead tag is a visible, low-cost correction. A mistakenly sent appointment cancellation, refund, payroll change, or inventory adjustment may require customer recovery, financial reconciliation, and manual repair across connected systems. If an action creates a commitment outside the business, or changes a record other people rely on, move it up a tier.
Low risk does not mean unattended by default; it means lighter automation controls for small businesses are usually proportionate. Restrict the workflow to its narrow task and sample its output. Medium-risk workflows should make proposed changes visible before release or provide a clear review queue. High-risk workflows should have tightly bounded access and a deliberate approval point before action, especially when AI workflow automation drafts or selects a customer-facing outcome.
Record the tier beside every workflow and reassess it whenever its permissions, connected systems, audience, or data inputs expand. That simple classification becomes the decision mechanism for later choices about access, approval, accountability, and evidence, not a label applied once and forgotten.
Control What Automations Can Access With Least-Privilege Permissions
Create a dedicated, named service account for each automation rather than connecting it through an employee’s login. A service account is an identity used only by a workflow, so its access can be reviewed, disabled, or replaced without disrupting a person’s work. Shared credentials are the weak alternative: several people may know the password, actions cannot be cleanly attributed, and offboarding one employee may require rebuilding every connection that used it.
Apply least privilege: grant only the systems, actions, and records required for the defined job. Role-based access control makes this practical by assigning a role, such as “lead-routing bot” or “invoice-draft workflow”, with a fixed permission set instead of giving it administrator access. Use single sign-on where the platform supports it, require multi-factor authentication for the people who administer connections, and store credentials in a controlled vault rather than inside a spreadsheet or workflow step.
| System | Narrow, useful scope | Scope to avoid by default |
|---|---|---|
| CRM | Read new-lead fields; create a task; apply one approved tag | Export all contacts, delete records, or alter user access |
| Accounting | Read invoice status; create a draft bill for review | Issue payments, change bank details, or post final entries |
| Help desk | Read ticket subject and category; assign a queue | Close disputes or send unrestricted customer replies |
| Ecommerce | Read order status and fulfillment state | Issue refunds, change prices, or access the full customer profile |
Write the permission boundary in four lines: allowed systems, allowed actions, allowed data fields, and access end date. For example, a dispatch workflow may receive an order number, service address, appointment window, and order status; it does not need payment details, complete purchase history, or every field in the customer record. That data-minimization choice limits what an AI workflow automation can expose or mishandle.
Start with read-only access when a workflow summarizes, routes, detects, or proposes. Add narrowly scoped write access only when the workflow must create a specific task, update a defined status, or add a standardized internal note. Use scoped API keys that permit those individual operations, rotate or replace credentials on a set schedule, and remove unused connections promptly. For temporary projects or vendors, set an expiration date from the outset. This makes automation oversight for small business manageable: each connection has a named purpose and a bounded ability to act.
Set Approval Thresholds That Preserve Speed Without Giving Up Control
For service businesses, automation is meant to remove repetitive bottlenecks and improve consistency; approval design keeps that speed from extending to decisions that deserve judgment.
An approval threshold is a rule that routes a proposed action to one of three outcomes: run unattended, enter a review queue, or stop until an authorized person decides. Human-in-the-loop review means the reviewer receives the proposed action and its relevant context before it is committed. Use it for consequential or uncertain exceptions, not for every routine step.
Set the approval threshold using seven signals: dollar amount, customer impact, confidence score, data sensitivity, volume, novelty, and irreversibility. A familiar, reversible action based on complete records may run automatically. Queue an action when the confidence score falls below the accepted level, the volume is unusual, the request falls outside an approved pattern, or a customer could be materially affected. Block an action that changes payment destinations, alters pay data, exposes sensitive records, or makes an irreversible commitment without a safe review route.
| Action | Threshold | Approver | Escalation path |
|---|---|---|---|
| Refund | Auto-approve up to $100 when order, payment, and reason match defined rules | Customer-service lead for higher or mismatched requests | Owner for repeat, disputed, or exceptional refunds |
| Discount | Apply a pre-approved offer code within its price ceiling | Sales manager for nonstandard discounts | Owner for margin or contract-pricing exceptions |
| Customer message | Send an approved template for a clear, routine request | Review uncertain, complaint-related, or customized replies | Manager for promises about price, timing, or remedy |
| Vendor payment or payroll change | Prepare and validate; never release or post unattended | A separate authorized reviewer | Owner or finance lead for exceptions |
| AI operational recommendation | Create an internal task or ranked suggestion only | Operations lead reviews schedule, staffing, or customer changes | Owner when capacity or an agreement is affected |
Maker-checker means the person or workflow that prepares a payment, refund, or pay-rate change cannot also be its sole approver. Segregation of duties takes the same idea further: one role proposes, another validates, and another releases when practical. A bookkeeper may prepare a vendor bill, an operations manager may match it to completed work, and the owner may release payment. The weak alternative gives one administrator power to create a vendor, change bank details, and pay the invoice.
Write boundary rules in testable language: “Review refunds over $100, any refund without a matching order, and the third refund for the same customer within 30 days.” This approach to governing business automation preserves unattended speed for routine outcomes while reserving human judgment for loss, customer harm, and difficult-to-reverse errors.
Assign Named Owners for Decisions, Exceptions, and Rollback
Every workflow needs a person whose name remains attached to the outcome. The automation can execute steps, but it cannot own a revenue decision, customer promise, inventory error, or financial correction. For effective automation oversight for small business, keep a lightweight ownership matrix with four roles:
| Role | Owns | Practical test |
|---|---|---|
| Business owner | The intended business result, operating rules, and acceptable risk | Can explain why the workflow exists and when it should stop |
| Workflow operator | The daily queue, approvals, and routine exceptions | Receives work that cannot proceed normally |
| Technical maintainer | The configuration, connections, credentials, and controlled changes | Can diagnose a failed step without changing business policy |
| Escalation contact | Material customer, financial, or reputational decisions | Has authority to halt, correct, and communicate externally |
The business owner is accountable for whether an AI workflow automation produces the right operational result; the technical maintainer is responsible for keeping its machinery working. Those roles may be held by the same person in a very small company, but they should still be recorded separately. “The consultant built it” is a weak ownership signal. “Operations manager owns dispatch outcomes; office manager handles incomplete-job exceptions; provider maintains the integration; owner handles customer commitments” is usable managed AI operations.
Exception handling is the designed path for work outside the workflow’s normal rules. Define the trigger, the pause or routing action, the alert recipient, the decision record, and the safe restart point. Missing required fields, low AI confidence, a duplicate transaction, a policy conflict, or a failed integration should create a visible case rather than a silent retry. The operator should resolve, reject, or escalate the case; the workflow should resume only from the approved step, not repeat a financial or customer-facing action.
Specify recovery before launch. A kill switch disables new executions immediately when a pattern is unsafe; a rollback reverses a completed, reversible change. For example, pause an erroneous customer-message sequence and send a manager-approved correction; restore inventory quantities from the pre-update value; or stop a payment workflow, isolate the affected transaction, and route correction to the authorized finance contact. Where reversal is uncertain, use a manual fallback: staff complete the task from the source record while the workflow remains disabled. Customer-facing mistakes and financial exceptions should have an explicit escalation contact and response expectation, not an unattended error inbox.
Create Audit Trails That Explain What Happened and Why
A customer complaint should be answerable from one record: which workflow ran, what information started it, what it did, who authorized it, and whether anything unusual occurred. An audit log is the event-by-event history that provides this traceability. It is not a screen recording or a pile of raw system events; it is a readable account that lets an operator reconstruct a specific outcome.
For each execution, capture the workflow name and version; trigger and source-record reference; action requested and action completed; service account used; timestamps; approval ID and approver where required; exception, error, or override; and final outcome. A useful entry might read: “Refund Request v3.2 | 10:14 | ticket #4819 triggered | proposed $125 refund | approval AR-77 by J. Lee at 10:16 | finance-bot account issued refund at 10:17 | no exception | completed.” By contrast, “refund automation ran” cannot resolve a dispute over amount, authority, or timing.
Maintain a compact automation register alongside the activity log. The register describes the workflow’s standing design; the log records each run. One shared spreadsheet or internal page is sufficient when it contains the fields below.
| Register field | What it makes clear |
|---|---|
| Purpose, owner, and risk tier | Why the workflow exists, who owns the result, and how much control it needs |
| Permissions and dependencies | The service account’s allowed actions and the apps, forms, or integrations it relies on |
| Approval rule and rollback instructions | When a person must intervene and how to contain or reverse an incorrect result |
| Version, change log, and review date | What changed, who approved the change, and when the design must be reconsidered |
A change log should record the date, editor, version, reason, approver, and tested outcome for every meaningful modification. Without a version record, a team investigating an incorrect invoice cannot tell whether the fault came from the source data, the approval decision, or a rule changed last week. Small business automation governance becomes manageable when records are designed for those real investigations, not maintained as paperwork for its own sake.
Monitor Performance and Review Controls as the Business Changes
The register and log become useful only when someone uses them to spot drift. Monitoring asks whether a workflow ran, completed, and produced the expected operational result. Governance asks whether its current permissions, approval rules, owner, and change authority are still appropriate. A workflow can show a healthy completion rate while remaining poorly governed because it has acquired access it no longer needs or is applying an outdated approval threshold.
Use a light, repeatable cadence. Each month, the business owner and technical maintainer should review workflow performance, failures, overrides, approval delays, customer-impact incidents, cost, and estimated time saved. Each quarter, review service-account permissions, active credentials, connected data sources, approval thresholds, named owners, rollback steps, and the register entry. The tradeoff is deliberate: monthly checks catch operational friction quickly; quarterly control reviews prevent access and rules from quietly expanding without turning routine oversight into bureaucracy.
| Metric | Decision it should inform |
|---|---|
| Completion and error rate | Repair a failing integration, input rule, or handoff before increasing volume. |
| Override rate | Revisit the workflow rule when people routinely correct its output. |
| Approval delay | Adjust routing, approver coverage, or a threshold that is slowing ordinary work. |
| Customer-impact incidents, cost, and time saved | Decide whether the workflow is producing enough reliable value to retain, redesign, or limit. |
Treat repeated exceptions as design evidence, not simply a queue for more manual intervention. If dispatchers repeatedly override an automated job assignment because the workflow cannot recognize a technician’s certification or territory constraint, add that constraint to the input and test the revised rule. If exceptions are genuinely novel, retain the approval gate; if they are predictable, redesigning the process is the better form of ongoing automation optimization.
Run an immediate governance review after a customer-impact incident, a new data source or connected system, expanded permissions, a changed approval rule, a major workflow version, or a change in the people who own or approve the work. Record the decision, the tested result, and any revised risk tier in the register. This keeps managed AI operations focused on controlled improvement rather than unattended change.
A 30-Day Rollout Plan for Governing Existing Automations
Use the first month to establish a baseline, not to redesign every workflow. Begin with the automations that send customer messages, issue refunds or invoices, change employee or payroll records, alter inventory or schedules, or handle sensitive data.
- Days 1–5: Inventory every active workflow, its trigger, connected systems, service account, and business purpose. Flag unknown owners and shared credentials.
- Days 6–10: Assign a risk tier and named business and technical owners. Disable abandoned workflows and remove access beyond each workflow’s defined task.
- Days 11–15: Set approval thresholds for high-impact actions. A refund may require a manager above a set amount; a lead tag can run automatically.
- Days 16–20: Record the exception route, kill switch, rollback method, and approver coverage for each priority workflow.
- Days 21–25: Enable execution, approval, override, and change logs; test one normal run and one failure or rollback scenario.
- Days 26–30: Schedule monthly performance checks and quarterly control reviews, then resolve remaining ownership or access gaps.
The milestone is a usable register for every priority workflow: named owners, bounded access, a decision rule, traceable activity, and a recovery path. Automation governance for small businesses should create controlled operational confidence, not slow business process automation with a policy document that nobody revisits.
Frequently Asked Questions
-
What is automation governance for a small business?
Automation governance is the control layer around a workflow that defines what it can do, when a person must approve it, how actions are recorded, and who responds to errors. Controls should increase with the workflow’s access, potential impact, reversibility, and data sensitivity.
-
How should small businesses assign risk tiers to automated workflows?
Assess each workflow by its system access, the impact of an error, how easily actions can be reversed, and the sensitivity of the data it handles. Low-risk tasks such as lead tagging can run with lighter controls, while high-risk actions such as refunds, payroll changes, account access changes, or customer commitments need tight permissions and approval gates.
-
How do I give an automation access without sharing an employee login?
Create a dedicated, named service account for each workflow and grant only the systems, actions, and data fields needed for its job. Use scoped API keys, credential vaults, multi-factor authentication for connection administrators, and expiration dates for temporary access.
-
Which automated actions should require human approval?
Require approval for actions involving financial authority, sensitive data, customer commitments, unusual volume, low confidence, or effects that are difficult to reverse. For example, refunds can auto-approve up to $100 only when the order, payment, and reason match defined rules, while higher or mismatched refunds go to a customer-service lead.
-
What is the difference between automation monitoring and automation governance?
Monitoring checks whether a workflow ran, completed, and produced the expected result. Governance checks whether its permissions, approval thresholds, owners, credentials, and rollback procedures remain appropriate, with monthly performance reviews and quarterly control reviews recommended.